Alerts & Updates
Key news and regulatory shifts that actually affect your products.
14 posts · page 1 of 2
October 2026 Patch Tuesday: Microsoft Fixes a Record 1,413 Flaws as AI-Assisted Research Adds to Discovery
Microsoft’s fix list is now 45 percent longer than last month’s record. Four Critical SAP fixes, including one scoring 10.0, land in the same week.
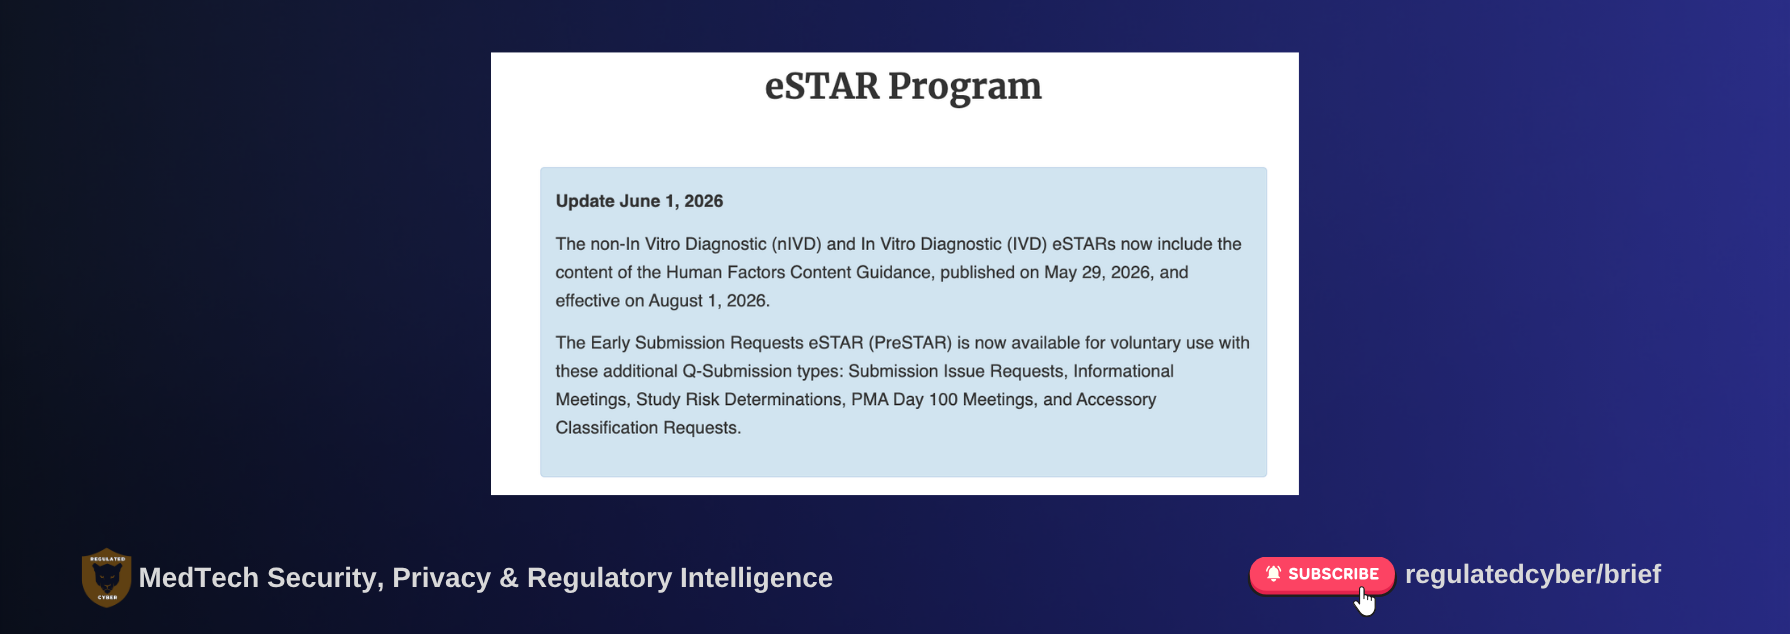
FDA's updated eSTAR Template: Which Version to Use, What Changed, and What to Do If You Already Have an AI Letter
eSTAR 6.2 was retired on August 3, 2026. New submissions belong on 7.1, files under review stay where they are, and one unchanged cybersecurity question still triggers technical screening holds.
FDA issues draft guidance on its electronic submission template for medical device PMA applications
FDA has proposed electronic-template standards for original PMAs and selected supplements, with mandatory use deferred until after final guidance and a transition period. Device regulatory and product-security teams should assess submission workflows without treating the draft…
CISA Retires the Weekly Vulnerability Bulletin on 28 September. Your Postmarket Triage Should Already Be Risk Based
FDA points device manufacturers at the same KEV Catalog and a high CVSS score is not a reason to drop everything
Android Security Bulletin September 2026 Patches 180 Flaws, Three Critical Remote Code Execution Bugs in NFC and One in Bluetooth
Three of the critical remote code execution fixes sit in the NFC module and one in Bluetooth, and no companion app can compensate for a radio stack compromised beneath it
Patch Tuesday, September 2026: Microsoft's Largest Release on Record, and a Flaw at the Bottom of the SAP Stack
Two Windows flaws were being exploited before the fix existed. SAP's most serious item this month runs before the system has checked who you are, and it sits under nearly every SAP product a manufacturer owns.
What IMDRF's New PCCP Document Actually Requires, and Where Cybersecurity Fits
The final N90 document from the Software as a Medical Device Working Group names five essential principles and three mandatory elements. One line about the impact assessment pulls security risk into every planned software change
FDA Wants to Hear From You on Generative AI-Enabled Medical Devices, and the Clock Is Running
CDRH has put prompt injection, agentic tool use, and foundation model drift into a proposed premarket evidence framework. Comments close 19 October 2026, and product security teams should not leave this to regulatory affairs alone.
Oracle Ships 943 Patches in August 2026 Update, More Than 460 Exploitable Without Credentials
No clinical or medical device product is named anywhere in the release, but Fusion Middleware, Hyperion, and E-Business Suite all run underneath systems that hold patient and manufacturing quality data
A Dataset From the March LiteLLM Compromise Now Names More Than 2,500 Exposed Organisations
Five months after the malicious packages were pulled from PyPI, CloudSEK has published the list. The credentials were taken from build systems, the machines that assemble and publish software
Patch Tuesday, August 2026: Microsoft Clears More Than 400 Actionable Flaws, SAP Patches a CVSS 10
Attackers were already exploiting one Windows flaw before Microsoft shipped the fix. SAP patched a CVSS 10 in Commerce Cloud, plus two flaws in the platform that links factory equipment to ERP
Thermo Fisher Patches Genetic Analyzer Flaw That Let DNA Test Files Be Altered Without a Trace
A researcher used Claude to alter a DNA test file in 45 minutes. Standard lab software did not notice. Thermo Fisher fixed the flaw on July 31, but three older product lines will never get a patch.
Explore other pillars
MedTech Security & Privacy
Practical insights for medical device and digital health environments.
Articles on threat modeling, secure development, and vulnerability management for the teams responsible for keeping regulated medical products secure across the total product lifecycle, from premarket design through postmarket surveillance.
AI & Cyber Awareness
Spot the AI-powered attack before it reaches your patients, products or people.
Practical articles on deepfakes, AI-driven phishing and social engineering in healthcare, securing AI-enabled medical products, and the awareness habits that keep clinical and product teams one step ahead, set against the EU AI Act and evolving global AI governance.
Career Growth
Build a product security career that compounds over time.
Mentorship, strategy, and hard-won perspective for professionals navigating the product security and MedTech cybersecurity space, whether you are breaking in, levelling up, or building your own platform.