Clarity for Regulated Product Teams
The Mission
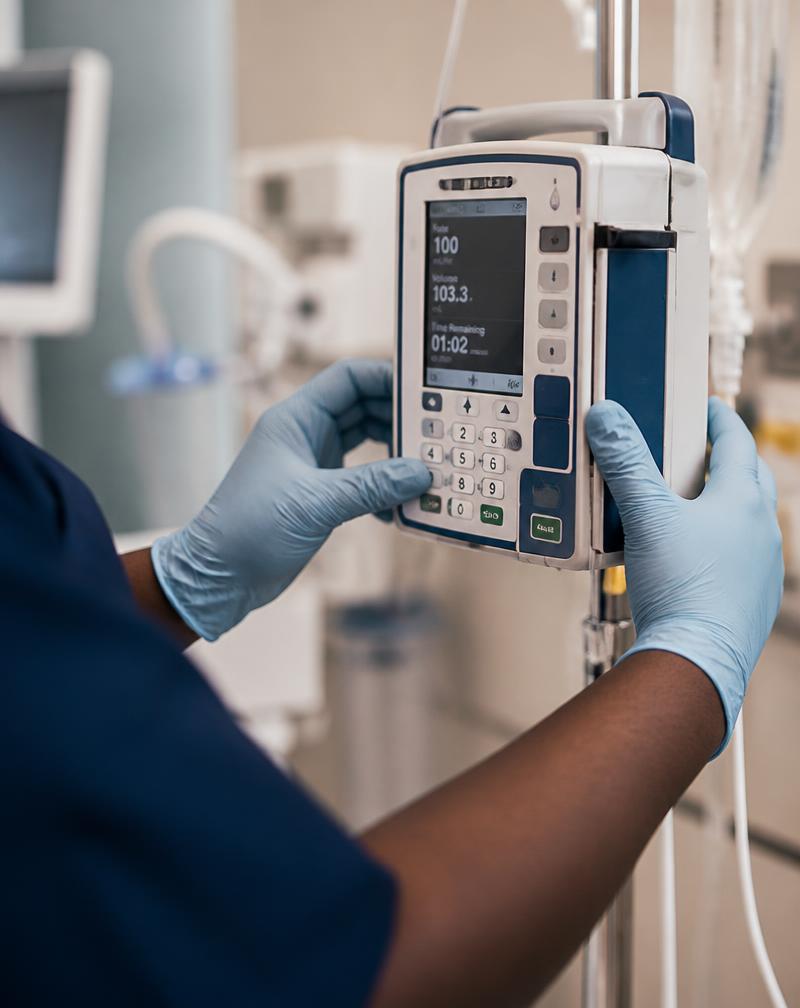
As people live longer, the technology supporting their health has to keep advancing with them. Devices and digital health products are more connected than ever, increasingly powered by AI, and they carry some of the most sensitive information a person has. That combination raises the stakes considerably. Attacks against healthcare and MedTech are rising, increasingly shaped by AI-enabled patterns that move faster than traditional defenses can keep up with. At the same time, the agencies overseeing these products, from the FDA's premarket and postmarket cybersecurity guidance to EU MDR obligations, HIPAA, and the emerging EU AI Act, continue to raise the bar, often with real deadlines and real consequences attached.
None of this happens in the abstract. Behind every device and every piece of guidance are product teams trying to ship something real, on a real timeline, while the ground keeps shifting under them. Keeping up means tracking multiple agencies, multiple frameworks, and a threat landscape that doesn't wait for the next audit cycle. That's a lot to carry alone, and most teams don't have the time to piece it together from a dozen scattered sources while also doing the actual work of building and securing their products.
Regulated Cyber exists to help close that distance. The publication brings together practical insight, clear guidance, and timely alerts on what's changing across MedTech cybersecurity, AI security, and the regulatory landscape that shapes them, so product security, engineering, and compliance teams have what they need to act, not just another article to read.
Who It's For
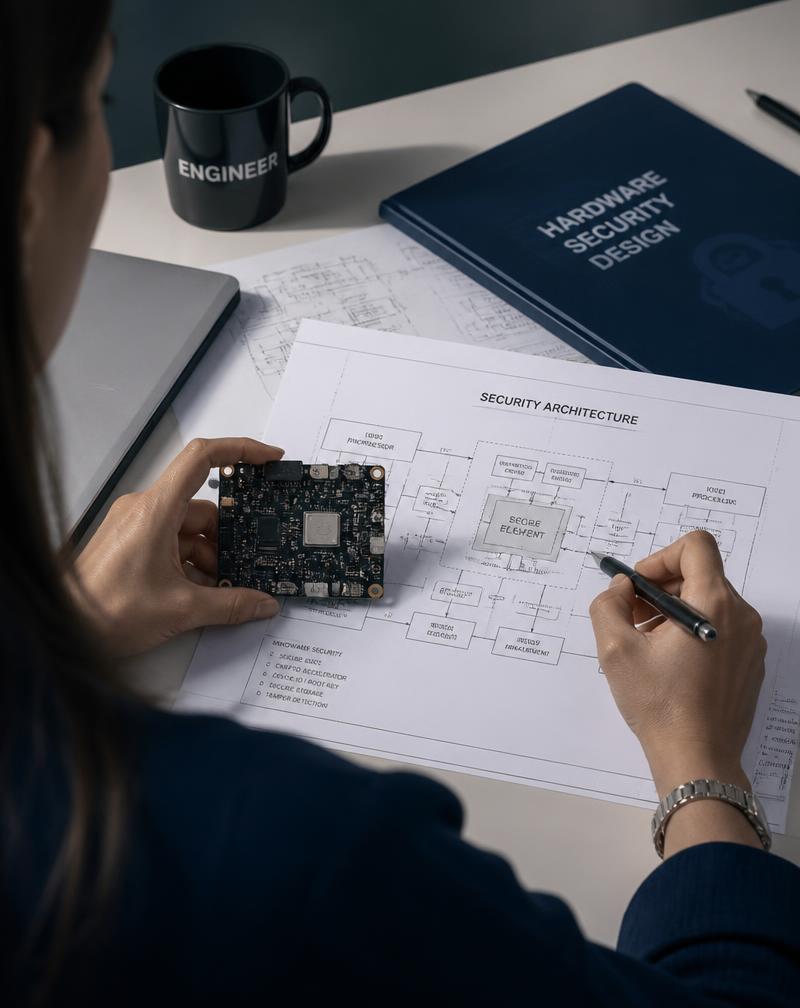
- Product security professionals & engineers
- Medical device & digital health teams
- Regulatory, quality & compliance teams
- Anyone tracking MedTech & AI security
Key focus areas
MedTech Security & Privacy
The technical and regulatory realities of building secure, trustworthy health products.
AI & Cyber Awareness
How AI reshapes the threat landscape, from deepfakes and AI phishing to the products themselves, and how teams stay alert.
Regulatory Updates
Agency and framework changes translated into what they mean for the people implementing them.
Career Growth
For product security professionals building their own path through this field.
Stay informed
Get MedTech cybersecurity, regulatory updates, and AI security developments in your inbox.
Free. Unsubscribe anytime. Your email always stays private.